Compliance that
traces itself.
CertAstra connects every risk to the controls, policies, and evidence that prove it's handled continuously, not once a year. Built for ISO 27001, SOC 2, GDPR, NIS2, the EU AI Act, ISO 9001, EU MDR, and Cyber Resilience Act.
Or schedule a personal demo →✓ Free plan, free forever ✓ No credit card required ✓ Upgrade anytime
the actual data model not a mockup
Built for the people who own security, risk & compliance
One framework becomes six spreadsheets.
Six becomes chaos.
A single ISO 27001 control needs a policy, an evidence file, an owner, and a review date. Multiply that by 93 controls in one framework then by every other framework you're also expected to run and compliance stops being a security practice. It becomes a tracking problem.
Untracked, disconnected, manual
One connected system
Risk, controls, policies, and evidence —
one connected system.
Every risk in your register links to the controls that mitigate it. Every control links to the policy that governs it and the evidence that proves it. Change one, and you can see exactly what else it touches instead of updating five documents by hand. Explore a step below.
Register
Compliance
A risk drives which controls exist. Each control is backed by a policy and proven by evidence.
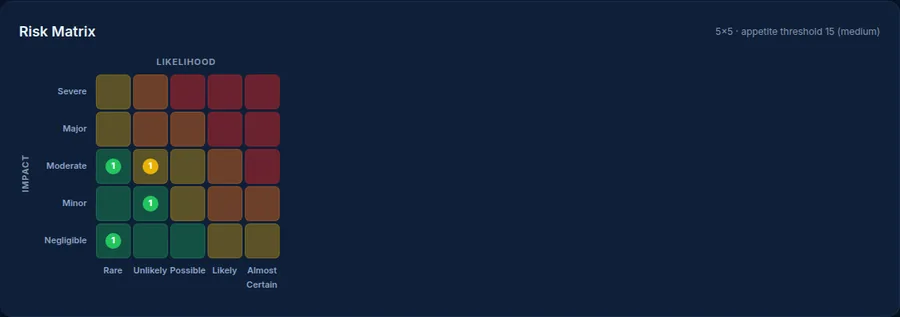
risk register - scored, matrixed, and linked to controls
A copilot that knows your organization
CertAstra's AI drafts answers to security questionnaires, runs gap analysis against any framework, and generates compliance documentation grounded in your organization's own context, not a generic template.
- AI-suggested answers for security questionnaires
- Framework-specific gap analysis
- AI-generated compliance documents
- Every output flagged for human review before it counts as evidence
Your posture doesn't go stale between audits
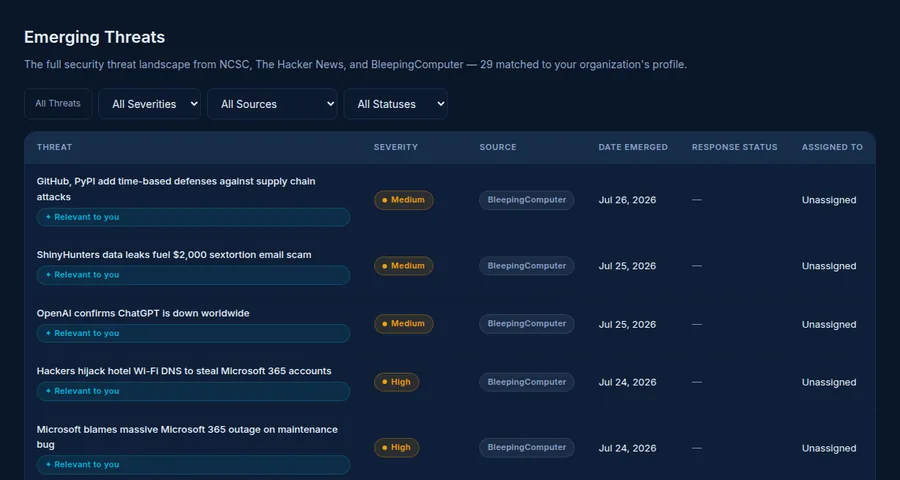
Emerging-threat intelligence is matched to your organization's own profile, and relevance is re-scored the instant your profile changes — not once a year, during a scramble before an audit.
- Emerging threats matched to your organization
- Instant relevance re-scoring on profile changes
- Live readiness view, not a static snapshot
Evidence that's linked, versioned, and never silently expired
Upload evidence directly against a control, track it through submission and review, and see expirations coming instead of finding out during the audit.
- Version history and a full review workflow
- Direct control linkage not a loose file folder
- Expiration tracking with advance visibility
A risk register that actually drives your controls
Configure your own risk matrix and methodology, log risks against real assets, and link each one straight to the controls mitigating it so risk management and control implementation stay in sync instead of living in separate documents.
- Configurable risk matrix & methodology
- Risk-to-control linkage
- Corrective actions & findings tracked to resolution
Manage every framework from the same workspace
Import ISO 27001, SOC 2, GDPR, NIS2, the EU AI Act, ISO 9001, EU MDR or Cyber Resilience Act — all eight are live today and keep your Statement of Applicability alongside them, without switching tools.
- 8 frameworks, ready to import today
- Statement of Applicability built in
- 281 controls, 815 questions, already mapped
A compliance copilot, not a chatbot.
Ask what a control needs, and CertAstra works the problem the way an auditor would.
One control. Every framework it satisfies.
Map a control once, and CertAstra tracks every framework that shares the same requirement so you implement it once and demonstrate it everywhere it applies, instead of re-proving the same control separately for each framework.
Illustrative example — your actual mappings depend on which frameworks you run
From first risk to audit-ready proof.
Managed like a project, or run like a system.
- Spreadsheets and shared drives
- Email chains to chase down evidence
- Manual reminders and trackers that go stale
- A scramble before every audit
- One connected risk → control → evidence system
- Evidence requested and tracked in-platform
- Continuous relevance & readiness scoring
- Audit-ready any day — not just audit week
Built the way a security buyer expects.
Built for the people who own the outcome.
CertAstra is built for the teams accountable for getting frameworks implemented and audits passed not just the auditors who show up once a year.
Simple, transparent pricing
Plans for every stage of your compliance programme. All prices in USD.
Get started with one framework
- 1 compliance framework
- Up to 3 users
- 2 GB storage
- Evidence management & audit workflows
- No AI features
1 month free
For small teams working towards certification
- 4 compliance frameworks
- Up to 10 users
- Up to 10 threat seats included
- 8 GB storage
- Automatic control mapping
- AI readiness summary
- Suggested controls
- AI risk register extraction
1 month free
For teams running several frameworks
- 6 compliance frameworks
- Up to 15 users
- Up to 10 threat seats included
- 15 GB storage
- All AI features in Starter
- AI policy generation
1 month free
Unlimited compliance operations
- Unlimited frameworks
- Unlimited users
- Up to 10 threat seats included
- 50 GB storage
- All AI features in Growth
- AI evidence review
- Audit answer assistance
- AI auditor assessment
- Control documentation drafting
- Security questionnaire automation
- Emerging threat assessment
- Draft answers from your policies
Tailored plans for large companies and audit firms
- Everything customised to your organisation
- AI features tailored to your needs
Compare plans
| Plan | Free | Starter | Growth | Enterprise | Custom |
|---|---|---|---|---|---|
| Frameworks | 1 | 4 | 6 | Unlimited | Unlimited |
| Users | 3 | 10 | 15 | Unlimited | Unlimited |
| Threat seats | — | 10 | 10 | 10 | 10 |
| Storage | 2 GB | 8 GB | 15 GB | 50 GB | Unlimited |
| AI features | |||||
| Automatic control mapping | Not included | Included | Included | Included | Included |
| AI readiness summary | Not included | Included | Included | Included | Included |
| Suggested controls | Not included | Included | Included | Included | Included |
| AI policy generation | Not included | Not included | Included | Included | Included |
| AI evidence review | Not included | Not included | Not included | Included | Included |
| Audit answer assistance | Not included | Not included | Not included | Included | Included |
| AI auditor assessment | Not included | Not included | Not included | Included | Included |
| Control documentation drafting | Not included | Not included | Not included | Included | Included |
| Security questionnaire automation | Not included | Not included | Not included | Included | Included |
| Emerging threat assessment | Not included | Not included | Not included | Included | Included |
| Draft answers from your policies | Not included | Not included | Not included | Included | Included |
| AI risk register extraction | Not included | Included | Included | Included | Included |
| Customised AI features (tailored to your needs) | Not included | Not included | Not included | Not included | Included |
For certification bodies and audit firms
Run every client audit from one workspace.
Assurance is for organisations that audit other companies — certification bodies, audit firms and independent auditors. Each client gets its own secure workspace, managed by your firm. Your clients answer questions and upload evidence; your auditors assess, raise findings and issue ISO-style reports under your brand.
- Multiple auditor seats
- Firm dashboard: every client, audit and finding in one view
- Reports with your firm's logo and name
- Records kept for completed audits
- Multiple clients, each fully isolated
- Client staff invited as auditees, at no extra cost to them
- Questionnaires, evidence requests and findings per client
Your clients don't need their own CertAstra plan — everything runs under your firm's Assurance subscription.
Auditing a company that already uses CertAstra? They can invite you directly — no plan needed.
Prices in USD. Prices exclude VAT. VAT added where applicable.
Annual plans: 12 months for the price of 11. Questions? Contact our team →
Frequently asked questions
Turn compliance from a recurring project
into a continuous capability.
Start free, or see it running on a real account.
Free plan, free forever · No credit card required